How We Work

At the NCCoE, we bring together experts from industry, government, and academia to address real-world needs for securing complex IT systems and protecting the nation’s critical infrastructure.  Together, we generate technical descriptions of the problems and map the desired solution to NIST and industry standards and best practices.  Along the way we seek comments from the public to make the problem descriptions as broadly applicable as possible and invite technology vendors to collaborate with us. 

Define

We define a scope of work with industry to solve a pressing cybersecurity challenge. 
Business person expressing opinions to junior and senior colleagues in conference room

We invite members of the community to talk about their challenges, ask questions, and listen to understand the challenge at hand. During this phase, we publish a draft project description for public comment. We adjudicate the comments and publish a final version to our website that outlines the cybersecurity challenge along with a draft architecture.  

Assemble

We assemble teams of industry organizations, government agencies, and academic institutions to address all aspects of a cybersecurity challenge. 
Business person expressing opinions to junior and senior colleagues in conference room

As of November 2026, we publish collaboration opportunities on the NCCoE’s CRADA Consortium Announcements page and SAM.gov. In the announcement, we explain what capabilities we are looking for. Potential collaborators respond with a completed Letter of Interest (LOI). Submitted LOIs are accepted on a first-come basis. Selected collaborators who join our projects will sign a Cooperative Research and Development Agreement (CRADA) to provide their hardware, software, and/or expertise.  All our work is open, transparent, publicly accessible, and informed by both the general public and technology providers. 

Build
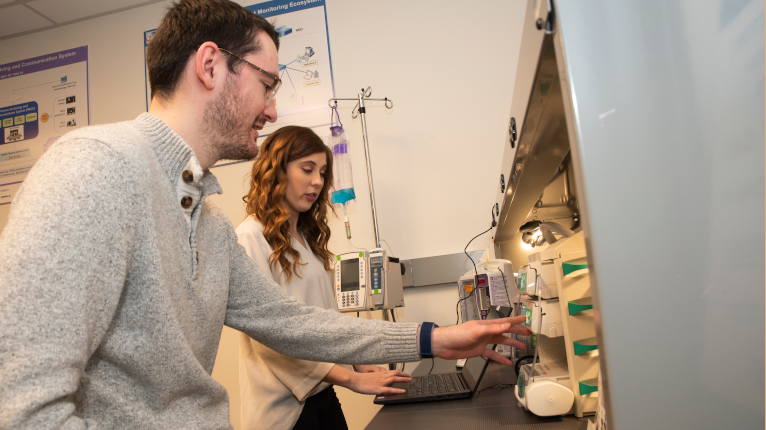
A photo of NCCoE Engineers working in the Healthcare lab.

We build a practical, usable, repeatable implementation to address the cybersecurity challenge. During this phase, a reference architecture is finalized. The collaborators provide support to install and configure their technologies and then they provide support throughout the build to address issues, such as interoperability. 

Keys to Our Success

Every step of our approach to creating practical cybersecurity solutions includes the following three key elements: 

Collaborate
The NCCoE relies on regular, robust collaboration with experts and innovators from various sectors in addition to the broader technology community to help us best identify and address businesses’ most pressing cybersecurity challenges.

Document
The NCCoE documents its work across multiple formats, including NIST publications, interactive guides, blogs, and videos. The outputs from our work include mappings of capabilities to the NIST Cybersecurity Framework (CSF) and detailed guidelines for organizations to implement similar architectures.

Advocate and Educate
Promoting what we do and how we do it, and helping organizations improve their cybersecurity posture, is foundational to everything we do at the NCCoE.